- Binance says an iOS flaw could let malicious apps access other apps’ files, potentially exposing wallet credentials.
- The risk depends on how wallets protect their secrets; accessing a file does not automatically reveal every wallet’s keys.
- Apple’s published update notes do not explicitly confirm a fix.
Binance has warned iPhone users that a flaw in Apple’s operating system could put crypto wallet credentials within reach of malicious applications installed on their devices.
The Nov. 10 warning concerns worse_query, a vulnerability that bypasses restrictions normally separating one app’s files from another.
Wallet Security Depends on More Than App Isolation
An iPhone wallet relies in part on iOS to prevent unrelated applications from accessing its private files. At the same time, a sandbox escape weakens that boundary, potentially exposing sensitive information stored within reach.
The consequences depend on what those files contain.
An unencrypted recovery phrase, for example, could give an attacker control of the associated wallet.
Apple’s Keychain security documentation describes additional protections for sensitive information.
Keychain items are encrypted, access is controlled through app entitlements, and access to secret values involves the Secure Enclave.
However, the worse_query research does not provide a wallet-by-wallet assessment or demonstrate that Keychain protections have been defeated.
A hardware wallet can create an additional layer of separation by keeping signing keys outside the phone.
Ledger’s documentation, for example, describes transactions being signed within its device’s Secure Element before the signed transaction is returned to the connected phone or computer.
In that arrangement, reading the companion app’s files would not, on its own, yield a signing key held on the separate device.
Binance Warns iPhone Users Over Wallet Security Flaw
Binance warned that worse_query affects iOS 26.7.1, 27.0.1, and 27.2, potentially allowing malicious apps to read files belonging to other applications.
“This is an iOS-level issue, not unique to Binance,” the exchange said.
Researcher forcequitOS published the proof-of-concept code on GitHub, listing support for iOS 26.0–26.7.2 and iOS 27.2.
The repository says it can access application-data folders and shared app storage.
The alert follows Binance’s earlier warning about FomoPeek, an iPhone app that SlowMist said contained malicious code capable of exposing wallet credentials.
Binance advised users in September to remove apps installed from untrusted sources and update iOS and their applications to the latest official versions.
Anyone who suspects a compromise should transfer funds to a new wallet created on a clean device and reset active login sessions, the exchange said.
Apple Update Leaves Fix Status Unconfirmed
Apple released iOS 27.2.1 on Nov. 9, addressing vulnerabilities involving App Intents, Bluetooth and Messages.
However, its security notes do not explicitly confirm that there is a fix for worse_query.
Binance nevertheless urged users to update iOS and their applications through official channels and remove applications obtained from untrusted sources, including sideloaded or manually signed packages.
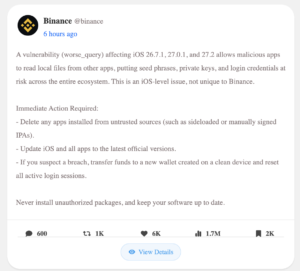
For users who suspect compromise, the exchange advised transferring assets to a new wallet created on a clean device and resetting active login sessions.
The requirement for a new wallet matters: importing an exposed recovery phrase into another app would preserve the same credentials an attacker may already possess.